
Firewalls
We build and maintain the parsers for every perimeter and internal device.
Onboarded & parsed
Managed SIEM gives you the platform, the tuning, and the people. We deploy Aqua SIEM into your estate, own the detection engineering, and watch it around the clock so your team never has to staff a night shift.
Noise from a firewall policy change suppressed at source, no ticket raised.
Impossible-travel sign-in confirmed, session revoked, your on-call notified at 03:29.
Shift notes and the overnight incident write-up waiting in your inbox.
One escalation reached your team. The rest closed before morning.
We onboard each source, write the parsers, tune the rules, and keep the coverage current as your estate changes.
We build and maintain the parsers for every perimeter and internal device.
Onboarded & parsedDeployment support, health monitoring, and coverage gap reporting.
Agent & EDRAuthentication and privilege detections tuned to your access patterns.
IdP & ADControl-plane and flow log onboarding across every account you run.
AWS, Azure, GCPBespoke applications parsed by our engineers, not left to your developers.
Custom parsersPhishing and delivery signals correlated with endpoint and identity events.
Mail gatewayFeed curation and IOC enrichment handled on your behalf.
Managed feedsNew detections added and false positives retired as part of the service.
Continuously tunedOur analysts watch your alerts around the clock, so nights, weekends, and holidays are covered without a rota of your own.
We write, tune, and maintain the correlation rules for your estate, retiring noisy detections instead of leaving them to you.
Our engineers deploy collectors, build parsers, and validate every log source against a defined onboarding plan.
A named lead who knows your environment, runs your monthly service review, and escalates when it matters.
Retention, log integrity, and audit reporting maintained to the frameworks you are certified against.
Verified incidents reach your team with context and recommended actions, or trigger agreed containment on your behalf.
Onboarding is run by our engineers to a fixed plan. You get coverage in weeks, not a year-long platform project.
We map your estate, agree the log sources in scope, set retention and compliance requirements, and define your escalation paths.
Our engineers stand up collectors, onboard each source, build the parsers, and validate that events arrive complete and on time.
Detections are baselined against your environment over the first weeks, with noisy rules retired before you ever see them.
The service runs 24/7 — alerts triaged by our analysts, verified incidents escalated to you, and coverage reviewed with your service lead each month.
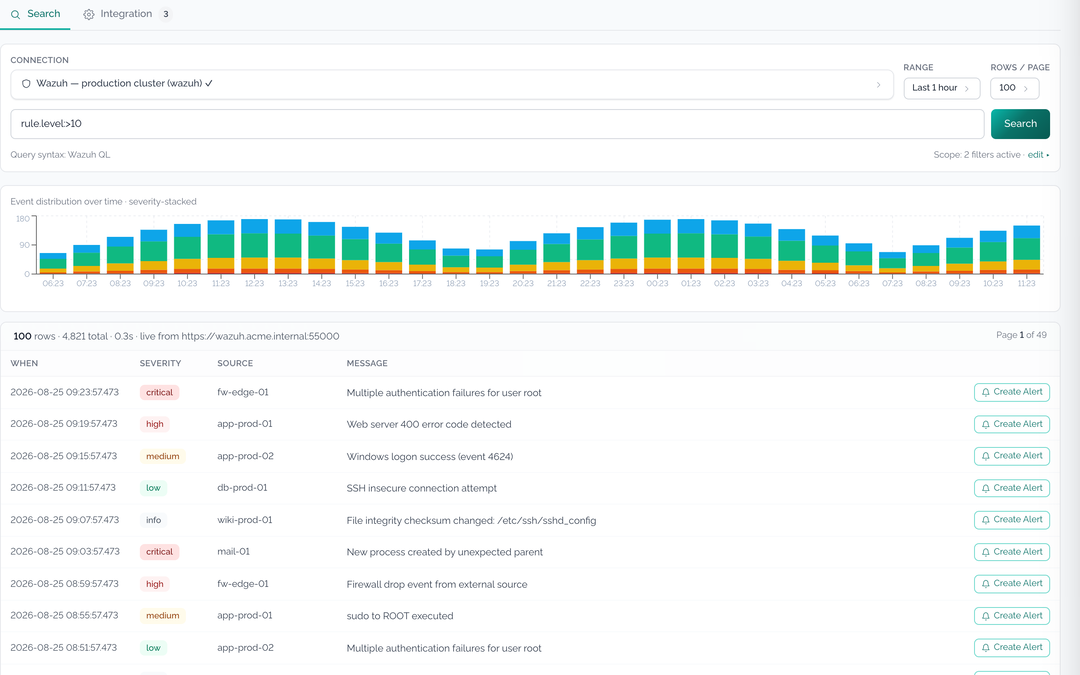
Managed SIEM is built for teams who need enterprise detection without hiring an enterprise SOC — lean IT functions, regulated mid-market firms, and security teams that need their nights and weekends covered.
Platform, deployment, detection engineering, 24/7 monitoring, and monthly service reviews under one agreement.


