
Commercial Feeds
Vendor intelligence on active campaigns, malware families, and infrastructure.
Premium sources
Aqua TIP aggregates global threat feeds, enriches every indicator with context, and delivers intelligence that is actually relevant to your industry and estate.
Open, commercial, and community sources are de-duplicated, scored, and correlated into a single stream your tools can consume.
Vendor intelligence on active campaigns, malware families, and infrastructure.
Premium sourcesPublic advisories, national CERT bulletins, and community indicator lists.
OSINT & CERTsLeaked credentials, initial access brokers, and chatter naming your brand.
Forums & marketsBehavioural detonation results with extracted indicators and TTPs.
Sandbox verdictsExploit availability and in-the-wild activity mapped to your exposed assets.
CVE & exploitIntelligence shared within your industry and geography, kept current.
Industry ISACsNewly registered lookalike domains and phishing kits impersonating you.
Kits & lookalikesConfidence scoring, de-duplication, and relevance ranking for your estate.
Scoring engineCommercial, open source, and community intelligence aggregated and de-duplicated into a single normalised stream.
Every indicator arrives with confidence score, first and last seen, related infrastructure, and mapped ATT&CK techniques.
Track the groups active in your sector — their tooling, targets, and current campaigns — in maintained actor profiles.
Intelligence is filtered against your industry, geography, and technology stack so analysts read only what applies.
Push indicators straight into SIEM, EDR, and firewalls via STIX/TAXII and API, so intelligence becomes prevention.
Analyst-written briefings and executive summaries covering emerging threats relevant to your organisation.
Aqua TIP runs continuously — collecting, scoring, and pushing intelligence into the controls that act on it.
Commercial, open source, dark web, and sector feeds are collected continuously and normalised into one indicator schema.
Indicators are de-duplicated, scored for confidence, and linked to actors, malware families, and ATT&CK techniques.
Relevance is judged against your sector, geography, and asset inventory, so what surfaces is what could actually reach you.
Indicators are pushed to SIEM, EDR, and network controls over STIX/TAXII or API, and briefings go to the people who need them.
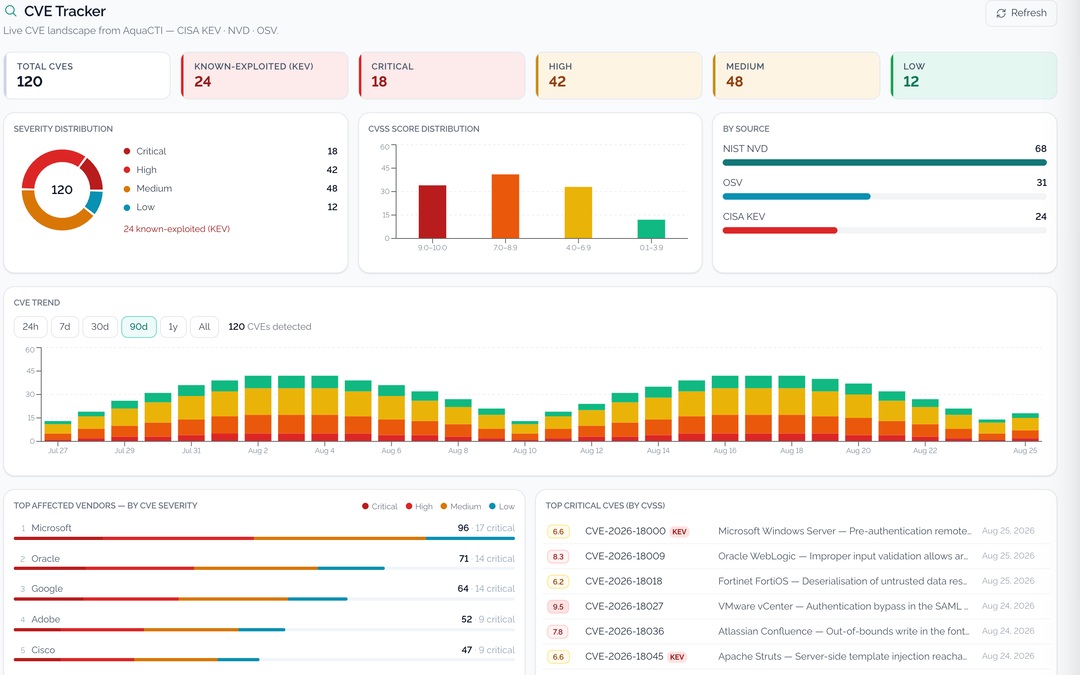
Aqua TIP is built for teams who need intelligence they can act on — feeding detections, briefing leadership, and prioritising what to fix first.
Curated feeds, actor profiling, IOC enrichment, and automated distribution to the controls that block them.


