
Endpoints
Process, file, and registry activity from every managed workstation and server.
EDR telemetry
Aqua Secure SOC empowers your analysts with AI SecOps — automated investigation, smart case management, and threat hunting — so they can focus on what matters.
Telemetry from across your estate lands in one console, correlated by AI and triaged before it reaches an analyst.
Process, file, and registry activity from every managed workstation and server.
EDR telemetryFirewall, proxy, and DNS traffic inspected for command-and-control patterns.
Flow & DNSSign-ins, privilege changes, and impossible-travel detection across your IdP.
Auth eventsControl-plane audit logs and misconfiguration signals from every account.
AWS, Azure, GCPBusiness application and API activity correlated with infrastructure events.
App & API logsMalicious attachments, impersonation attempts, and reported messages.
Phishing signalsEvery alert enriched with global indicators, actor context, and severity.
Live IOC feedsAutonomous agents investigate, enrich, and recommend before handover.
L0–L3 triageContinuous monitoring across your entire environment with AI that learns your baseline and flags true anomalies.
Detected threats auto-create structured incidents with context, severity, and recommended actions pre-filled.
Analysts get timeline views, entity graphs, and enriched indicators to investigate threats in minutes, not hours.
Track incidents from open to closed with assignment, notes, evidence, and SLA timers built in.
Automate containment actions — isolate endpoints, block IPs, revoke sessions — triggered by AI verdicts.
Proactively hunt for indicators of compromise across your environment using hypothesis-driven investigation.
The SOC runs around the clock. AI handles the volume, your analysts handle the judgement calls.
Telemetry from endpoints, network, identity, cloud, and email is ingested and correlated in real time against behavioural baselines and live threat intelligence.
AI agents score and de-duplicate alerts, discard the noise, and promote genuine threats into structured incidents with context attached.
Analysts work from timeline views and entity graphs, with enriched indicators and related events already gathered on the case.
Containment runs on approval or automatically — isolate an endpoint, block an IP, revoke a session — and every action is logged on the case.
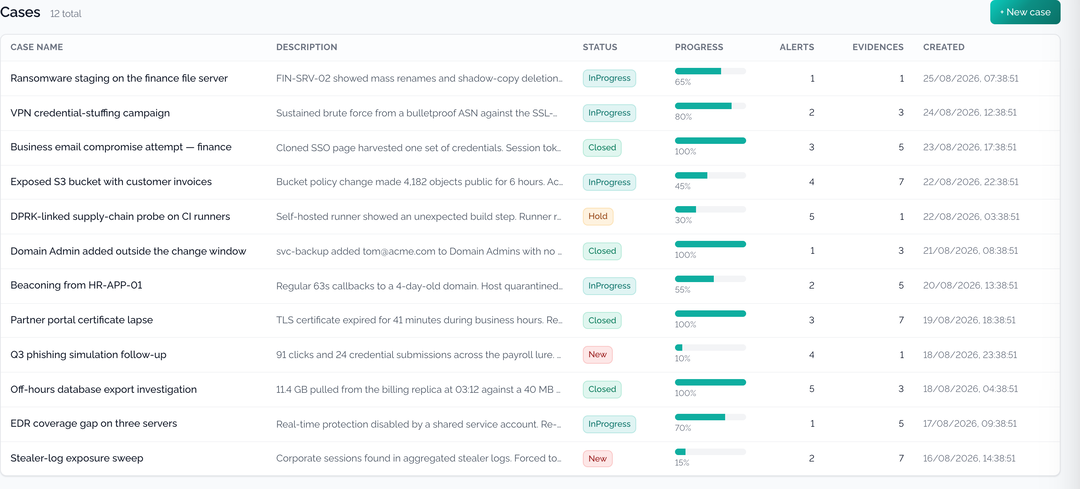
Aqua SOC is built for security teams who need real results, not just dashboards — whether you run a two-person team or a 200-person enterprise SOC.
Empower your team with AI triage, automated containment, threat hunting, and real-time monitoring.


