
Firewalls
Perimeter and internal firewall traffic, denies, and policy changes.
Syslog / CEF
Aqua SIEM gives your team a single pane of glass across all log sources — with AI-powered correlation that surfaces real threats, not noise.
Ingest from anything that writes a log, normalise it once, and query it all from one place with sub-second indexing.
Perimeter and internal firewall traffic, denies, and policy changes.
Syslog / CEFWindows, macOS, and Linux event logs alongside EDR detections.
Agent & EDRAuthentication, MFA, and directory changes from your identity provider.
IdP & ADControl-plane audit trails, flow logs, and storage access events.
AWS, Azure, GCPBusiness applications, web servers, and database audit logs.
App & DB logsDelivery, quarantine, and phishing verdicts from your mail security.
Mail gatewayIndicators matched against every event as it is indexed.
IOC enrichmentShip anything else over the ingest API with your own parser.
API & webhookCollect and index logs from any source — firewalls, endpoints, cloud, apps — with sub-second ingestion.
AI-powered rules engine correlates events across sources to detect multi-stage attacks and lateral movement.
Pre-built and customisable dashboards give SOC analysts instant visibility into alert severity, trends, and status.
Automated compliance reports for GDPR, PCI-DSS, ISO 27001 — always audit-ready, zero manual effort.
Define alert thresholds, severity levels, and escalation paths. Notify via email, Slack, or webhook.
Fully managed SIEM option — Aqua Secure AI handles all tuning, maintenance, and monitoring 24/7.
Aqua SIEM ingests, parses, and correlates continuously — so detections fire on behaviour, not on a single noisy event.
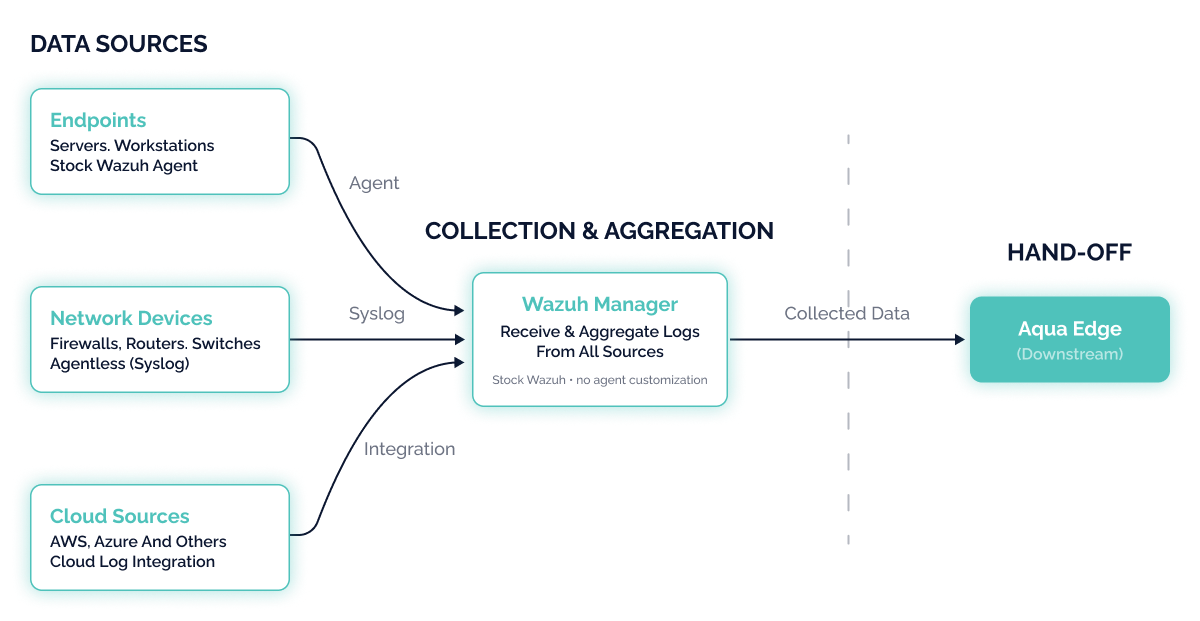
Agents, syslog, cloud APIs, and the ingest API bring every log source into one pipeline with sub-second ingestion.
Events are parsed into a common schema and enriched with asset, identity, and threat intelligence context as they land.
The AI rules engine links related events across sources to expose multi-stage attacks and lateral movement rather than isolated noise.
Detections raise alerts on your thresholds and severity levels, routed to the right responder by email, Slack, or webhook.
Aqua SIEM is built for teams that need answers from their logs fast — from a lean IT function to a 200-person enterprise SOC, self-managed or fully managed by us.
Sub-second ingestion, AI correlation, custom alerting, and compliance reporting in one platform.


