
Aqua SIEM Native
Indicators matched against every event as it is indexed, with retro-hunting on new intel.

The threat intelligence platform behind every Aqua Secure product.
Fifty-plus global feeds collected, scored, and correlated in one place — then pushed into your SIEM, your SOC console, and your network controls as indicators your tools can act on.
Every indicator lands scored, attributed, and mapped to ATT&CK before it reaches a console or a control.
Collect
Commercial, open source, dark web, sandbox, and sector feeds pulled continuously.
Normalise
De-duplicated into one indicator schema with first and last seen retained.
Score
Confidence, exploitability, and relevance to your estate combined into one score.
Distribute
Pushed to SIEM, EDR, and network controls over STIX/TAXII or API.
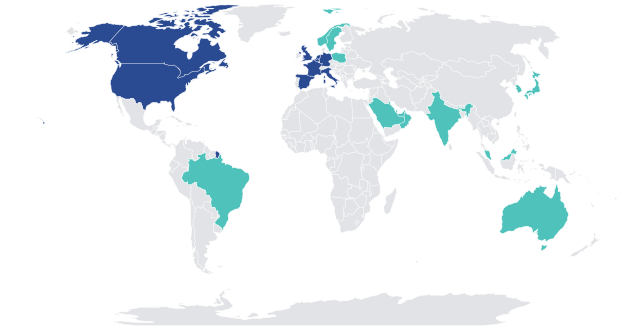
Global collection, local relevance. Indicators are ranked against your sector, geography, and asset inventory, so a campaign hitting your region and your technology stack outranks noise from the other side of the world.
Indicators matched against every event as it is indexed, with retro-hunting on new intel.
Alerts arrive pre-enriched with actor, campaign, and confidence context.
Standards-based feed any consuming platform can subscribe to.
Block lists and detection content pushed straight to enforcement points.
Intelligence-driven tasks raised in Jira or ServiceNow with full context.
REST API and webhooks for anything you have built in-house.
Fifty-plus curated sources, confidence scoring, actor attribution, and STIX/TAXII distribution into the tools you already run.