
ISO 27001
Full ISMS build, internal audit, and Stage 1 and Stage 2 support.
Certification
Our consultants take you from gap assessment to certificate — writing the policies, gathering the evidence, and sitting with you in the audit — with Aqua GRC holding the control set once you are certified.
Evidence collected automatically from cloud, identity, and endpoint systems each week.
Supplier reviews and two access recertifications, each with a named owner and due date.
Policies authored, approved at management review, and acknowledged by all staff.
Stage 1 audit booked for next month, on the original timeline.
Map a control once and reuse it across every framework you pursue. Your second certification costs a fraction of your first.
Full ISMS build, internal audit, and Stage 1 and Stage 2 support.
CertificationReadiness, observation window preparation, and auditor liaison.
Type I & IIROPAs, DPIAs, subject request handling, and processor agreements.
Compliance programmeRisk analysis and safeguard implementation for protected health data.
SafeguardsScoping, segmentation evidence, and QSA engagement support.
SAQ & RoCCurrent and target profile assessment with a costed roadmap.
Maturity upliftRegulatory baseline delivered alongside your existing certifications.
Regional baselineSecurity questionnaires and due diligence answered on your behalf.
QuestionnairesWe assess you against the standard before quoting the work, so the plan reflects your actual starting point.
A full policy set authored around how your business actually operates, not a template pack you have to rewrite.
Aqua GRC pulls evidence from your connected systems, so control operation is proven without screenshot marathons.
One consultant owns your programme end to end — and is in the room, or the call, for the audit itself.
The mandatory internal audit and management review are run for you, with findings closed before the external auditor arrives.
Controls stay evidenced between audits, so surveillance visits are routine rather than a scramble.
A named consultant runs the programme to a dated plan. You are not handed a spreadsheet and left to interpret the standard.
We scope the certification, assess you against every clause and control, and give you a dated plan with the effort split between our team and yours.
Policies, procedures, risk assessment, and the statement of applicability are authored around your business, then implemented with your owners.
Controls go live in Aqua GRC with evidence collected automatically, and we run the internal audit and management review the standard requires.
We prepare your team for the auditor, attend the audit, and manage any findings through to closure and certificate issue.
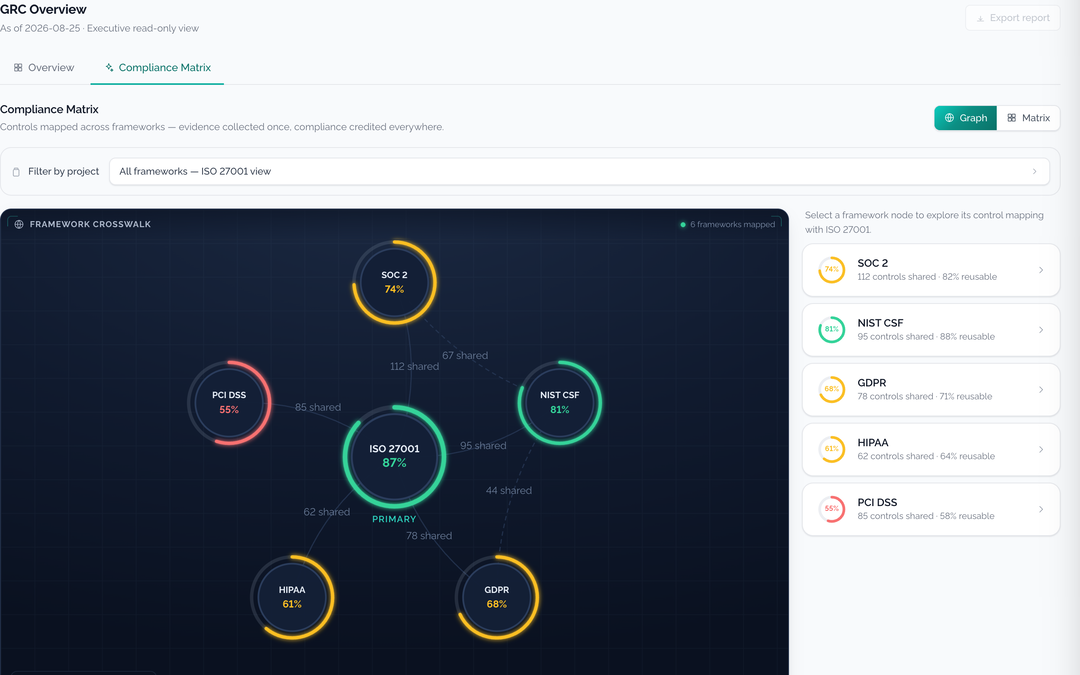
Managed compliance is built for teams facing certification without a compliance function — first-time ISO 27001, a customer demanding SOC 2, or a surveillance audit nobody has prepared for.
Gap assessment, policy authoring, evidence collection, internal audit, and auditor support under one engagement.


