
Credential Harvest
Cloned sign-in pages for the services your staff actually use every day.
Login lures
Phishbot runs realistic phishing simulations, delivers training the moment someone clicks, and shows you exactly how your human risk is changing over time.
Templates modelled on live phishing campaigns, localised and role-targeted, launched from one console and measured in one report.
Cloned sign-in pages for the services your staff actually use every day.
Login luresInvoice, CV, and delivery-note attachments that record who opened them.
Files & macrosExecutive and supplier impersonation asking for payments or data.
ImpersonationApproval-request lures that test whether staff rubber-stamp prompts.
Push & OTPText-message campaigns covering delivery, payroll, and IT support pretexts.
SMS luresQR codes in email and print that route to a simulated capture page.
QuishingScripted phone pretexts run against helpdesk and finance teams.
Voice pretextsLures written from public data about your brand, sector, and roles.
Tailored luresCampaign templates modelled on live phishing seen in the wild, localised by language and targeted by role.
Run continuous randomised campaigns across the year instead of one annual test everyone warns each other about.
Anyone who clicks lands on a short training moment explaining the exact cues they missed.
Assignable awareness modules with quizzes and completion tracking, mapped to compliance training requirements.
Every user, team, and department carries a risk score based on click, report, and training behaviour over time.
One-click reporting from the mail client sends suspected phishing straight into the SOC as a triaged alert.
Phishbot runs continuously in the background — campaigns land throughout the year, and training follows the mistake, not the calendar.
Pick templates by threat type and difficulty, target them by role, department, or language, and set the schedule for the year.
Campaigns are delivered gradually and randomised, so results reflect real behaviour rather than a warned-about test day.
Clicks trigger a short training moment immediately, and repeat behaviour assigns a longer module automatically.
Click rate, report rate, and time-to-report roll into per-user, per-team, and organisation-level risk scores you can trend and present.
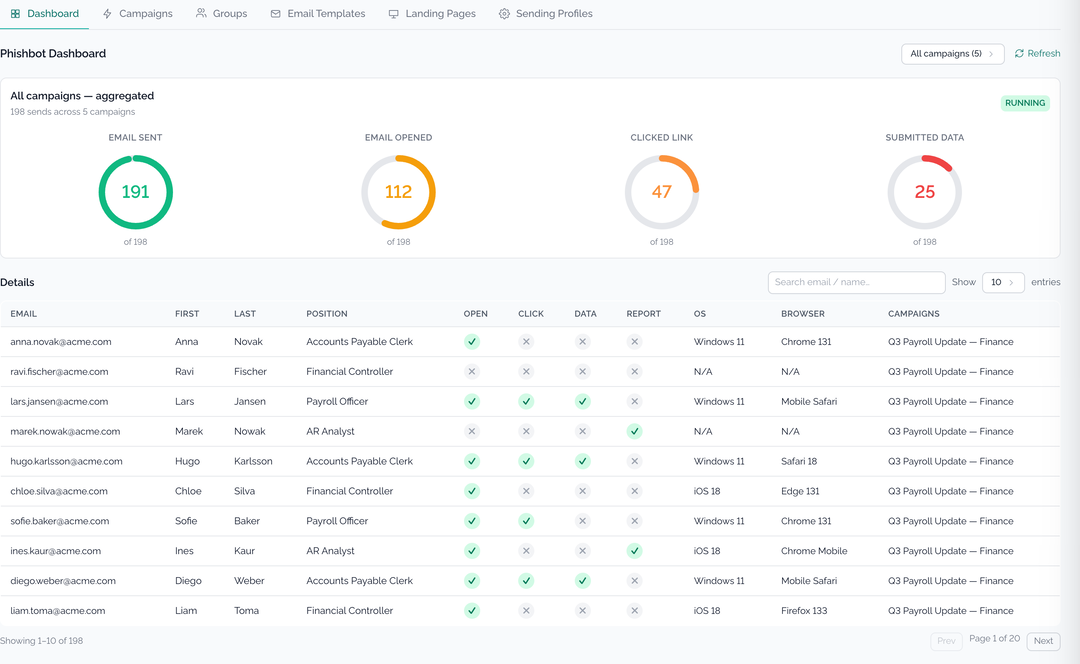
Phishbot is built for the teams answerable for awareness — security, HR, and compliance working from one set of numbers, from 50 staff to 50,000.
Realistic simulations, just-in-time training, human risk scoring, and board-ready awareness reporting.


