
Domains & DNS
Forgotten subdomains, dangling records, and takeover-prone entries.
Subdomain discovery
Attack Surface Management continuously discovers every domain, host, certificate, and exposed service attributed to your organisation — including the assets nobody told you about — and ranks what to fix first.
Remote management reachable from the internet on two acquired hosts and a test box.
Dangling DNS records pointing at deprovisioned cloud resources, takeover-prone.
Expiring certificates, weak TLS, and version disclosure across public web hosts.
Two of these were not on your asset inventory.
We map your external footprint from the outside in, attribute each finding back to your organisation, and re-scan continuously as it changes.
Forgotten subdomains, dangling records, and takeover-prone entries.
Subdomain discoveryInternet-reachable services, admin panels, and remote access left open.
Exposed servicesExpiring, self-signed, and mismatched certificates across your footprint.
TLS hygieneFrameworks and versions fingerprinted and matched to known vulnerabilities.
Tech & versionsPublic storage, open APIs, and orphaned cloud resources still reachable.
Buckets & APIsAssets registered outside IT and attributed back to your organisation.
UnattributedNewly registered domains and clones set up to imitate your brand.
ImpersonationSupplier and acquisition footprints that carry your exposure with them.
Supplier estateYour footprint is re-scanned from the outside continuously, so new exposure surfaces within hours of appearing.
Every finding is traced back to your organisation through registration, certificate, and infrastructure evidence.
Surface the assets nobody registered with IT — marketing microsites, test environments, and forgotten cloud accounts.
Exposed services are checked for known vulnerabilities, weak configuration, and missing controls.
Findings are ranked by exploitability, exposure, and business criticality — not by raw CVSS alone.
Assign owners, track fixes to closure, and re-scan to verify the exposure is genuinely gone.
Discovery runs continuously from outside your perimeter. New exposure is found, attributed, and ranked without anyone filing a ticket.
Starting from your known domains and IP ranges, we expand outwards through DNS, certificates, and infrastructure records to find everything reachable.
Each asset is tied back to your organisation with evidence, so you are not chasing exposure that belongs to someone else.
Services are fingerprinted and tested for known vulnerabilities, weak configuration, and expired or mismatched certificates.
Findings are ranked, assigned to owners, and re-scanned after the fix so closure is verified rather than assumed.
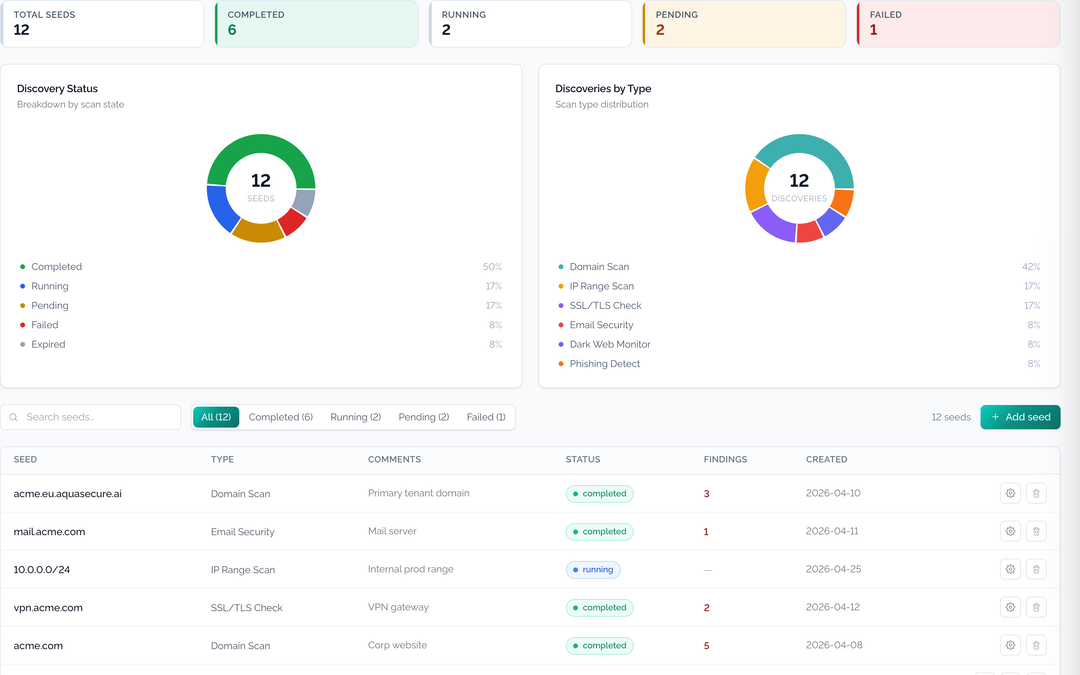
Attack Surface Management is built for teams accountable for an estate they did not fully build — after acquisitions, after years of shadow IT, and ahead of every audit.
Continuous external discovery, asset attribution, risk-based prioritisation, and remediation tracking through to verification.


