
ISO 27001
Full Annex A control mapping with evidence pulled from your connected estate.
93 controls
Centralise governance, risk, and compliance in one platform — with real-time audit readiness, automated evidence collection, and continuous monitoring.
Map one control once and satisfy it everywhere. Aqua GRC keeps every framework in sync as your evidence changes.
Full Annex A control mapping with evidence pulled from your connected estate.
93 controlsTrust services criteria tracked continuously across the observation window.
5 criteriaData protection obligations, records of processing, and subject request handling.
11 chaptersAdministrative, physical, and technical safeguards for protected health information.
54 safeguardsScoped monitoring of the cardholder data environment and its segmentation.
12 requirementsPosture across Identify, Protect, Detect, Respond, and Recover.
CSF + 800-53Regulatory baseline mapped to the same controls you already evidence.
Regional baselineAuthor a framework, import controls, and reuse existing evidence.
Your own controlsManage GDPR, HIPAA, PCI-DSS, ISO 27001, CTDISR, and custom frameworks from a single interface.
Automatically gather and organise evidence from connected systems — no manual screenshots or exports.
Real-time monitoring against framework controls with instant alerts when gaps appear.
Generate audit reports on-demand that map evidence to controls — reducing audit prep from weeks to hours.
Centralised risk register with treatment plans, owners, deadlines, and risk acceptance workflows.
Board-level dashboards showing compliance posture, risk trends, and top remediation priorities.
Aqua GRC runs continuously in the background. Connect once, and controls stay evidenced without a compliance sprint.
Link your cloud accounts, identity provider, endpoints, and ticketing tools through the connectors platform. No agents to roll out, no rip-and-replace.
Evidence is pulled on a schedule and mapped to the controls it satisfies across every framework you have enabled.
Controls are tested continuously. When a control drifts out of compliance, the owner is alerted with the failing evidence attached.
Export an audit package that maps evidence to controls, or share a live executive dashboard with the board.
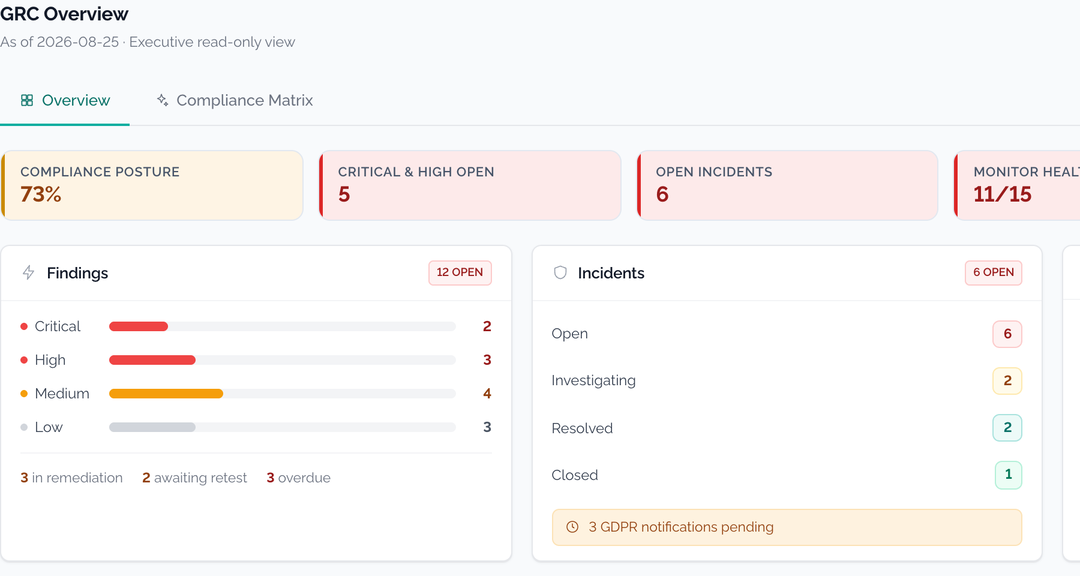
Aqua GRC is built for teams carrying audits alongside day-to-day security work — from a two-person compliance function to a 200-person enterprise programme.
Automated evidence collection, continuous control monitoring, and board-ready reporting in one platform.


